Does Your Guest Wi-Fi Actually Stay Outside the Company Network?
A Guest label is not an isolation test
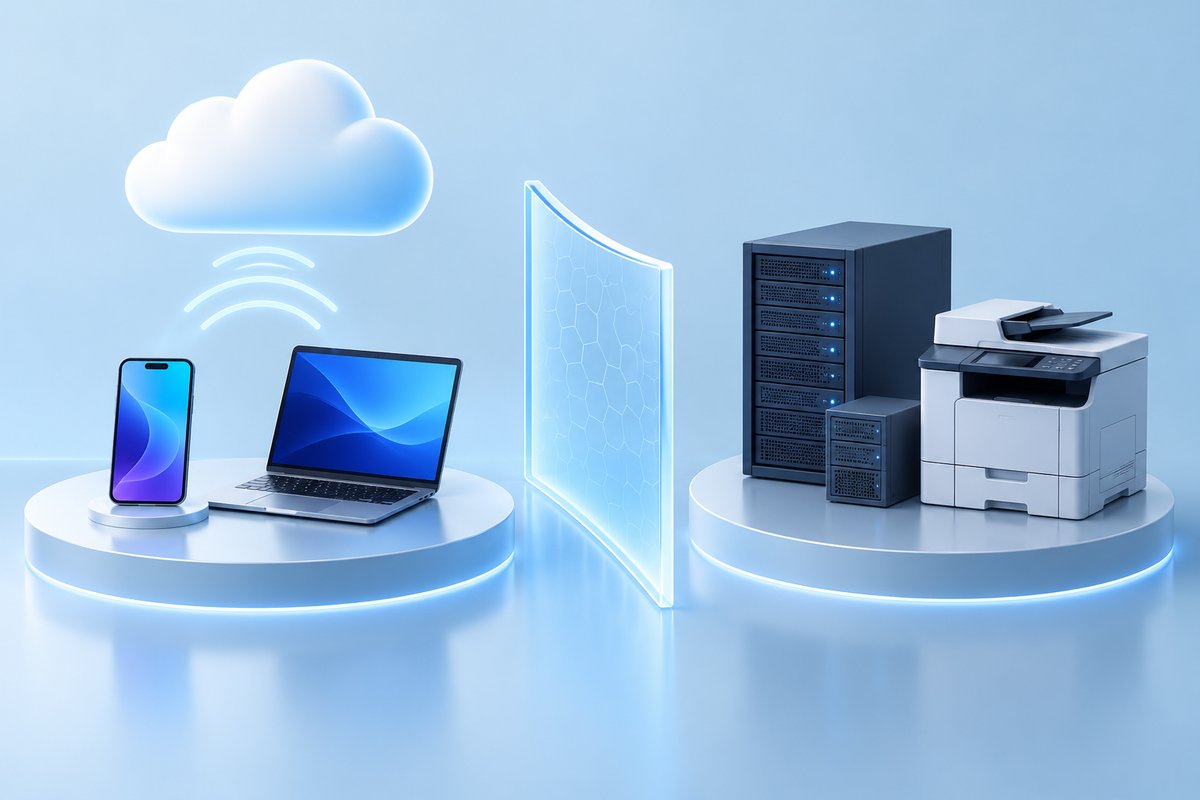
An office may advertise a guest Wi-Fi name while visitors can still reach its NAS, printer or router administration page. That does not meet the intended separation. An SSID identifies a connection choice; access to other systems depends on network configuration and permission rules. Verify actual paths before claiming guests cannot reach company systems.
The Canadian Centre for Cyber Security recommends zones using SSIDs, VLANs and access controls, and warns about defaults that allow traffic between zones. This is design guidance, not a claim that every device has identical menus or that creating a VLAN completes security. Consult the model documentation and identify where rules are enforced.
Define required access before writing rules
List sources and destinations: guests may need the internet but not accounting systems, file shares or device-management pages. Separate employee, visitor and specialised devices according to need. Do not assume every printer belongs in the same zone. If visitors need printing, specify the permitted service and owner instead of opening the entire company network.
Have the administrator map the access point, switches and router or firewall, recording each SSID’s zone and permitted cross-zone traffic. Separating guests from staff and preventing guests from communicating with one another are different requirements. Configure and test both when both are needed; one result cannot prove the other.
Test from a guest device and record both outcomes
Use an authorised test device connected only to guest Wi-Fi, with alternative paths such as a company VPN or LAN cable disabled to avoid confusion. Confirm external browsing works, then test administrator-approved internal services and management pages. Record the network, access point, time, destination and expected outcome. Avoid broad scanning or testing unauthorised systems.
Failure to reach an internal service must be attributable to isolation, not an offline service or failed name resolution. Have the administrator cross-check from the employee side and review firewall evidence. For example, if an offline NAS is unreachable by both guests and staff, that result does not prove separation. Include IPv6 paths when enabled rather than drawing a universal conclusion from IPv4 alone.
Keep exceptions narrow and reviewable
For a guest-access exception, record source, destination, service, reason, approver and review date. Test that the permitted task works and other access remains blocked. Recheck affected paths after router replacement, access-point additions or control changes; last year’s report does not establish the current configuration.
For Chawinnix network or security work within its published services, prepare a diagram, device models, required workflows and test results with unnecessary data removed. Segmentation reduces unwanted access but still depends on authentication, updates and destination-system permissions. It does not guarantee prevention of every incident.